Source: Unite.AI
An employee’s AI assistant can now do more than answer a question. It can connect to company systems, install extensions, run commands and build applications. For security teams, the challenge is deciding which of those actions should be allowed—and retaining the ability to intervene when the context changes.
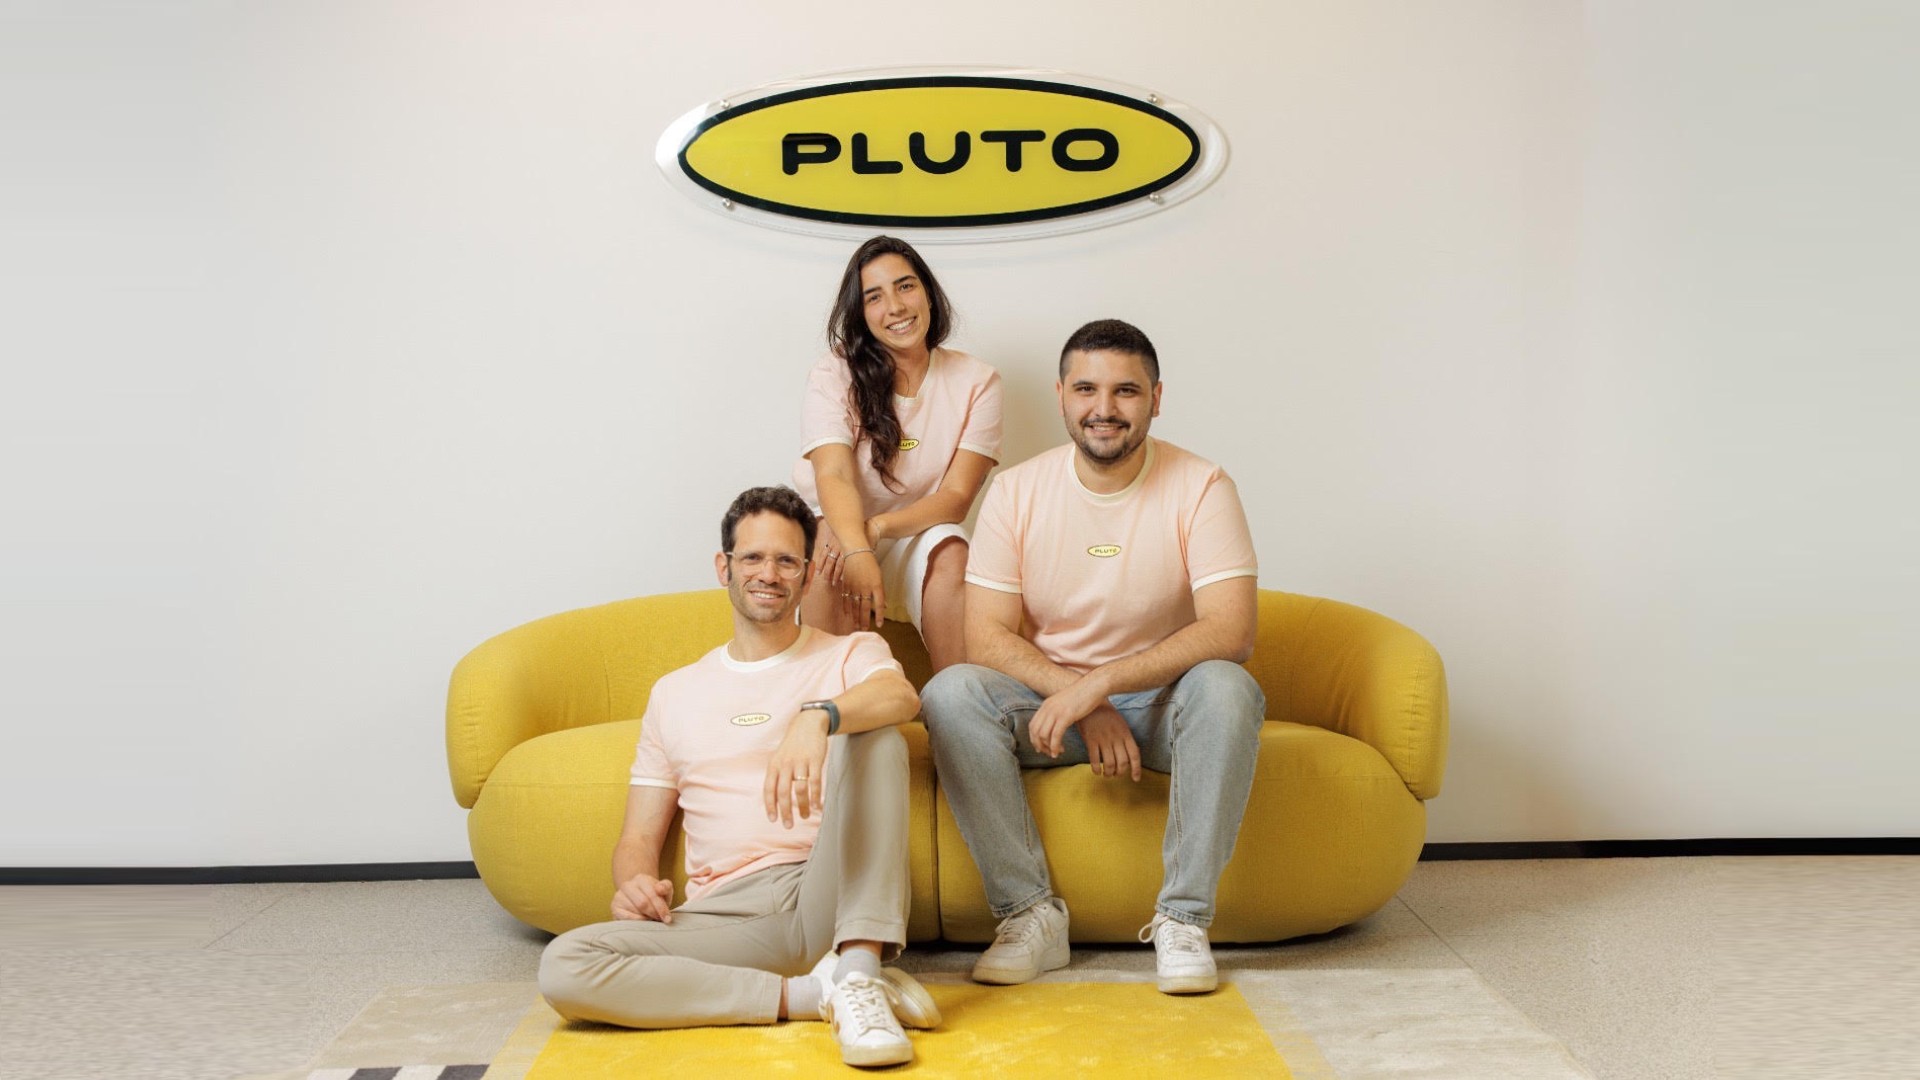
Pluto Security is emerging from stealth with $42 million in total funding to address that problem. The company announced an approximately $34 million latest financing round led by Jump Capital, following an earlier seed round led by TLV Partners. The announcement does not specify the stage of the latest round.
Founded in 2025, Pluto says it has reached multi-million-dollar annual recurring revenue, secures more than 1 million endpoints globally and serves more than 40 enterprise customers. Named customers include Oscar Health, Workato, Sixt and AlphaSense, alongside Fortune 500 organizations. The new capital will fund product development, security research and U.S. expansion.
The AI Workspace Becomes a Security Boundary
Pluto describes its category as AI workspace security. Its scope includes the AI tools employees use, the components connected to those tools, and the applications, agents and automations employees create.
That scope reflects a change in how software enters an organization. An employee can assemble a workflow from an AI assistant, a community skill and a connector to business data without going through a conventional development project. Each addition can change what the assistant can access or execute.
The Model Context Protocol, or MCP, is one example. It provides a way for AI applications to connect to tools and data sources. The security question extends beyond whether the AI application itself is approved: teams also need to understand the permissions and behavior of the servers and integrations it uses.
This is part of the broader software supply-chain challenge behind AI agent governance. Reviewing a model or an assistant in isolation leaves out dependencies that can influence its behavior or expand its reach.
Discovery, Risk Assessment and Runtime Control
Pluto says its platform combines endpoint visibility, contextual risk analysis and real-time enforcement. The aim is to give security teams enough information to restrict a dangerous action without automatically banning the entire tool that performs it.
Its website divides the platform into four functions: Explorer discovers AI activity; Risk Radar evaluates discoveries using its risk database; Space Shield applies enforcement policies; and Marketspace provides a curated collection of AI add-ons. The company describes coverage spanning tools, supply-chain components, runtime behavior and AI-generated artifacts.
Examples on the site include requiring approval before an agent accesses a payment API, restricting sensitive data access and allowing trusted MCP servers while quarantining others. These are descriptions of intended product behavior, rather than independently tested guarantees.
The distinction between discovery and enforcement matters. An inventory can tell a security team that a connector exists. Effective control also requires knowing what it can reach and being able to limit the relevant action. A permitted tool may still encounter an unsafe extension, an overprivileged credential or a task that exceeds the user’s authority.
Consider an assistant asked to summarize a customer record. Reading a permitted record and exporting an entire customer database are different actions, even if both originate in the same approved application. Contextual policies are intended to distinguish those situations. Their practical value depends on the accuracy of the observations and the reliability of enforcement.
Plutonium Examines the Components Around the Agent
A central part of Pluto’s approach is Plutonium, a free AI supply-chain security catalog powered, according to the announcement, by the company’s proprietary RisksDB. It helps practitioners assess components such as skills, extensions and MCP servers before adoption.
The public hub describes an agentic risk engine that combines publisher information, compatibility mapping, source review and code scanning. Its assessment categories include command execution, persistent access tokens, third-party data sharing, data modification and deletion. It also offers an MCP Inspector and safe-use guidance.
Those categories turn a broad question—whether an add-on is safe—into more concrete questions about capabilities and access. A connector that can read a document presents a different exposure from one that can modify records or execute commands. The same capability can also be appropriate for one business workflow and excessive for another.
A catalog assessment and runtime protection address different parts of the problem. Inspection can inform adoption decisions; ongoing controls must account for how a component is actually used. Neither should be mistaken for proof that every future action will be harmless.
Early Commercial Traction, With Results Still to Measure
Pluto’s reported customer and revenue figures suggest early demand for this category. The company says it has built its adoption around security research, free resources and practitioner participation, with thousands of professionals using and contributing to Plutonium.
Those adoption figures are company-reported. The release does not provide independent measurements of detection coverage, false positives, enforcement latency or attack prevention. Securing more than 1 million endpoints describes the reported scale of deployment; it does not establish that every possible AI workflow on those devices is covered.
For enterprise buyers, the operational questions are specific: which tools and execution paths are visible, which actions can be blocked, how exceptions are approved, and what evidence is retained when a policy intervenes. A system that stops risky activity but routinely interrupts legitimate work creates a different problem for the business.
A Security Team Building Around User Intent
CEO and co-founder Shahar Bahat founded Pluto with Tal Ofer Regev and Gil Maman. Bahat previously held cybersecurity leadership roles at Microsoft and Palo Alto Networks. Regev previously served as VP of R&D at Palo Alto Networks, while Maman spent more than six years in Israeli Military Intelligence in technical leadership roles. Pluto says it now employs more than 50 people across the United States and Israel.
Bahat frames the company’s approach around understanding what users are trying to accomplish and giving security teams the context to enable that work safely. The product challenge is translating that philosophy into precise, dependable controls as employees adopt new tools and assemble new workflows.
The funding announcement places Pluto in a growing contest to secure AI where it acts on enterprise systems. Its next test is demonstrating that discovery, component assessment and runtime enforcement can work together at the scale its early customer base already represents.